Orios Family Hotel
Home Rooms About us Beach & pool Restaurant Events Gallery Prices Contact
BGБългарски ENEnglish
Book now
Orios Family Hotel
Orios Family Hotel
+359 876 413 400 [email protected] Orios Family Hotel, 9 Lotos St, Primorsko, Bulgaria
F
BG| EN
  • Home
  • Rooms
  • About us
  • Beach & pool
  • Restaurant
  • Events
  • Gallery
  • Prices
  • Contact
  • Book now
+359 876 413 400 Facebook
Семеен Хотел Ориос

Privacy Policy

Document:Privacy Policy
Version:01
Date:1 April 2024

1. Introduction

This Privacy Policy is adopted pursuant to Regulation (EU) 2016/679 of the European Parliament and of the Council of 27 April 2016 on the protection of natural persons with regard to the processing of personal data and on the free movement of such data (the General Data Protection Regulation – GDPR).

Семеен Хотел Ориос is committed to protecting the personal data of its guests, employees, partners, and any other individuals whose data it processes. This policy sets out how the organisation collects, uses, stores, and protects personal data.

2. Material and Territorial Scope

This policy applies to the processing of personal data carried out in the context of the activities of Семеен Хотел Ориос, regardless of whether the processing takes place within or outside the European Union, provided it relates to the offering of goods or services to data subjects in the EU or the monitoring of their behaviour within the EU.

3. Definitions

  • Personal data – Any information relating to an identified or identifiable natural person (data subject). An identifiable natural person is one who can be identified, directly or indirectly, in particular by reference to an identifier such as a name, identification number, location data, online identifier, or one or more factors specific to the physical, physiological, genetic, mental, economic, cultural, or social identity of that person.
  • Sensitive data (special categories) – Personal data revealing racial or ethnic origin, political opinions, religious or philosophical beliefs, trade union membership, genetic data, biometric data for identification purposes, data concerning health, or data concerning a person’s sex life or sexual orientation.
  • Processing – Any operation or set of operations performed on personal data, whether or not by automated means, such as collection, recording, organisation, structuring, storage, adaptation, alteration, retrieval, consultation, use, disclosure by transmission, dissemination, alignment, combination, restriction, erasure, or destruction.
  • Controller – The natural or legal person, public authority, agency, or other body which, alone or jointly with others, determines the purposes and means of the processing of personal data.
  • Data subject – An identified or identifiable natural person whose personal data is processed.
  • Consent – Any freely given, specific, informed, and unambiguous indication of the data subject’s wishes by which they, by a statement or by a clear affirmative action, signify agreement to the processing of personal data relating to them.
  • Child – Under the GDPR, specific protections apply to children. In Bulgaria, the age limit for consent to information society services is 14 years.
  • Profiling – Any form of automated processing of personal data consisting of the use of personal data to evaluate certain personal aspects relating to a natural person, in particular to analyse or predict aspects concerning that person’s performance at work, economic situation, health, personal preferences, interests, reliability, behaviour, location, or movements.
  • Personal data breach – A breach of security leading to the accidental or unlawful destruction, loss, alteration, unauthorised disclosure of, or access to, personal data transmitted, stored, or otherwise processed.
  • Main establishment – The place of the controller’s central administration in the EU, or the place where decisions on the purposes and means of processing are taken, if different from the central administration.
  • Recipient – A natural or legal person, public authority, agency, or another body to which personal data is disclosed.
  • Third party – A natural or legal person, public authority, agency, or body other than the data subject, controller, processor, and persons who, under the direct authority of the controller or processor, are authorised to process personal data.

4. Policy Declaration

Семеен Хотел Ориос declares that it shall:

  • Process personal data lawfully, fairly, and in a transparent manner in relation to the data subject.
  • Collect personal data only for specified, explicit, and legitimate purposes and not further process it in a manner incompatible with those purposes.
  • Ensure that personal data is adequate, relevant, and limited to what is necessary in relation to the purposes for which it is processed.
  • Take every reasonable step to ensure that inaccurate personal data is erased or rectified without delay.
  • Keep personal data in a form permitting identification of data subjects for no longer than is necessary for the purposes for which the data is processed.
  • Process personal data in a manner that ensures appropriate security, including protection against unauthorised or unlawful processing and against accidental loss, destruction, or damage, using appropriate technical and organisational measures.

5. Obligations and Responsibilities

5.1 Data Controller

Семеен Хотел Ориос, as the data controller, is responsible for and must be able to demonstrate compliance with the data protection principles. The controller implements appropriate technical and organisational measures to ensure and be able to demonstrate that processing is performed in accordance with the GDPR.

5.2 Data Processor

Where processing is carried out on behalf of the controller, the controller engages only processors providing sufficient guarantees to implement appropriate technical and organisational measures so that processing meets the requirements of the GDPR and ensures the protection of the rights of the data subject.

5.3 Data Protection Officer (DPO)

Where required by applicable law, the organisation designates a Data Protection Officer. The DPO is involved, in a timely manner, in all issues relating to the protection of personal data, reports directly to management, and operates independently in the performance of their tasks.

6. Data Protection Principles

  • Lawfulness, fairness, and transparency – Personal data is processed lawfully, fairly, and in a transparent manner.
  • Purpose limitation – Data is collected for specified, explicit, and legitimate purposes and is not further processed in a manner incompatible with those purposes.
  • Data minimisation – Data collected is adequate, relevant, and limited to what is necessary.
  • Accuracy – Personal data is accurate and, where necessary, kept up to date.
  • Storage limitation – Data is kept in an identifiable form for no longer than is necessary.
  • Integrity and confidentiality – Data is processed with appropriate security measures in place.
  • Accountability – The controller is responsible for and must be able to demonstrate compliance with all of the above principles.

7. Rights of the Data Subject

Under the GDPR, data subjects have the following rights:

  • Right to information – The right to be informed about the collection and use of their personal data.
  • Right of access – The right to obtain confirmation as to whether personal data concerning them is being processed, and, where that is the case, access to the personal data.
  • Right to rectification – The right to obtain rectification of inaccurate personal data without undue delay.
  • Right to erasure (right to be forgotten) – The right to obtain the erasure of personal data under certain circumstances.
  • Right to restriction of processing – The right to obtain restriction of processing in certain cases.
  • Right to data portability – The right to receive personal data in a structured, commonly used, and machine-readable format and to transmit that data to another controller.
  • Right to object – The right to object to processing based on legitimate interests or for direct marketing purposes.
  • Rights related to automated decision-making and profiling – The right not to be subject to a decision based solely on automated processing, including profiling, which produces legal effects or similarly significantly affects the data subject.

8. Consent

Where processing is based on consent, the controller must be able to demonstrate that the data subject has given consent. Consent must be freely given, specific, informed, and unambiguous. The data subject has the right to withdraw consent at any time, and withdrawal must be as easy as giving consent.

9. Lawful Basis for Processing

Processing shall be lawful only if and to the extent that at least one of the following applies: the data subject has given consent; processing is necessary for the performance of a contract; processing is necessary for compliance with a legal obligation; processing is necessary to protect the vital interests of the data subject or another person; processing is necessary for the performance of a task carried out in the public interest; or processing is necessary for the purposes of the legitimate interests pursued by the controller or a third party.

10. Data Minimisation

The organisation ensures that personal data collected is adequate, relevant, and limited to what is necessary for the purpose for which it is processed. Unnecessary data is not collected or retained.

11. Accuracy

The organisation takes reasonable steps to ensure that personal data is accurate and, where necessary, kept up to date. Inaccurate data is erased or rectified without undue delay.

12. Storage Limitation

Personal data is retained only for as long as is necessary to fulfil the purpose for which it was collected. The organisation establishes retention periods for different categories of data and implements procedures for the secure deletion or anonymisation of data that is no longer required.

13. Integrity and Confidentiality

The organisation implements appropriate technical and organisational measures to ensure the security of personal data, including protection against unauthorised or unlawful processing and against accidental loss, destruction, or damage.

14. Transfer of Personal Data

Where personal data is transferred to a third country or international organisation, appropriate safeguards are in place in accordance with the GDPR, including but not limited to adequacy decisions, standard contractual clauses, or binding corporate rules.

15. Data Breach Notification

In the event of a personal data breach, the controller shall notify the competent supervisory authority without undue delay and, where feasible, within 72 hours of becoming aware of the breach. Where the breach is likely to result in a high risk to the rights and freedoms of natural persons, the data subjects concerned shall also be notified without undue delay.

16. Data Protection Impact Assessment (DPIA)

Where a type of processing, in particular using new technologies, is likely to result in a high risk to the rights and freedoms of natural persons, the organisation carries out an assessment of the impact of the envisaged processing operations on the protection of personal data prior to the processing.

17. Training

All employees who process personal data receive appropriate training on data protection principles and procedures. Training is provided at induction and at regular intervals thereafter to ensure continued compliance with this policy and the GDPR.

18. Guest conduct records (decision support)

Where you have stayed with us before, or booked and did not arrive, we may keep a short, dated record of specific events connected with your own booking or stay: a no-show, a cancellation inside the penalty window of the policy you booked under, a payment that was charged back or failed repeatedly, a balance left unpaid after departure, damage to our property, or misconduct recorded by our staff with a written note. Each record states what happened, when, the amount involved where money was concerned, and who or what recorded it. We use these records only to support a decision our staff take about a future booking – for example whether to ask for prepayment, a deposit, or a non-refundable rate. A member of staff always makes that decision; no decision about you is taken solely by automated means, and nothing is refused, priced or charged automatically. We never record or take into account your nationality, language, age or any special category of data, and we never add information obtained from outside our own relationship with you. Where this property belongs to a group of hotels under the same owner, and both hotels have chosen to do so, such a record may be visible to the other hotels in that group and to no one else. The legal basis is our legitimate interest in preventing loss and protecting our property and staff (Art. 6(1)(f) GDPR). Records are kept for 12 to 24 months from the event, as set by this property, and are then archived and deleted. You may ask to see the records held about you, to have an inaccurate record corrected, and to object to this processing on grounds relating to your particular situation.

Orios Family Hotel

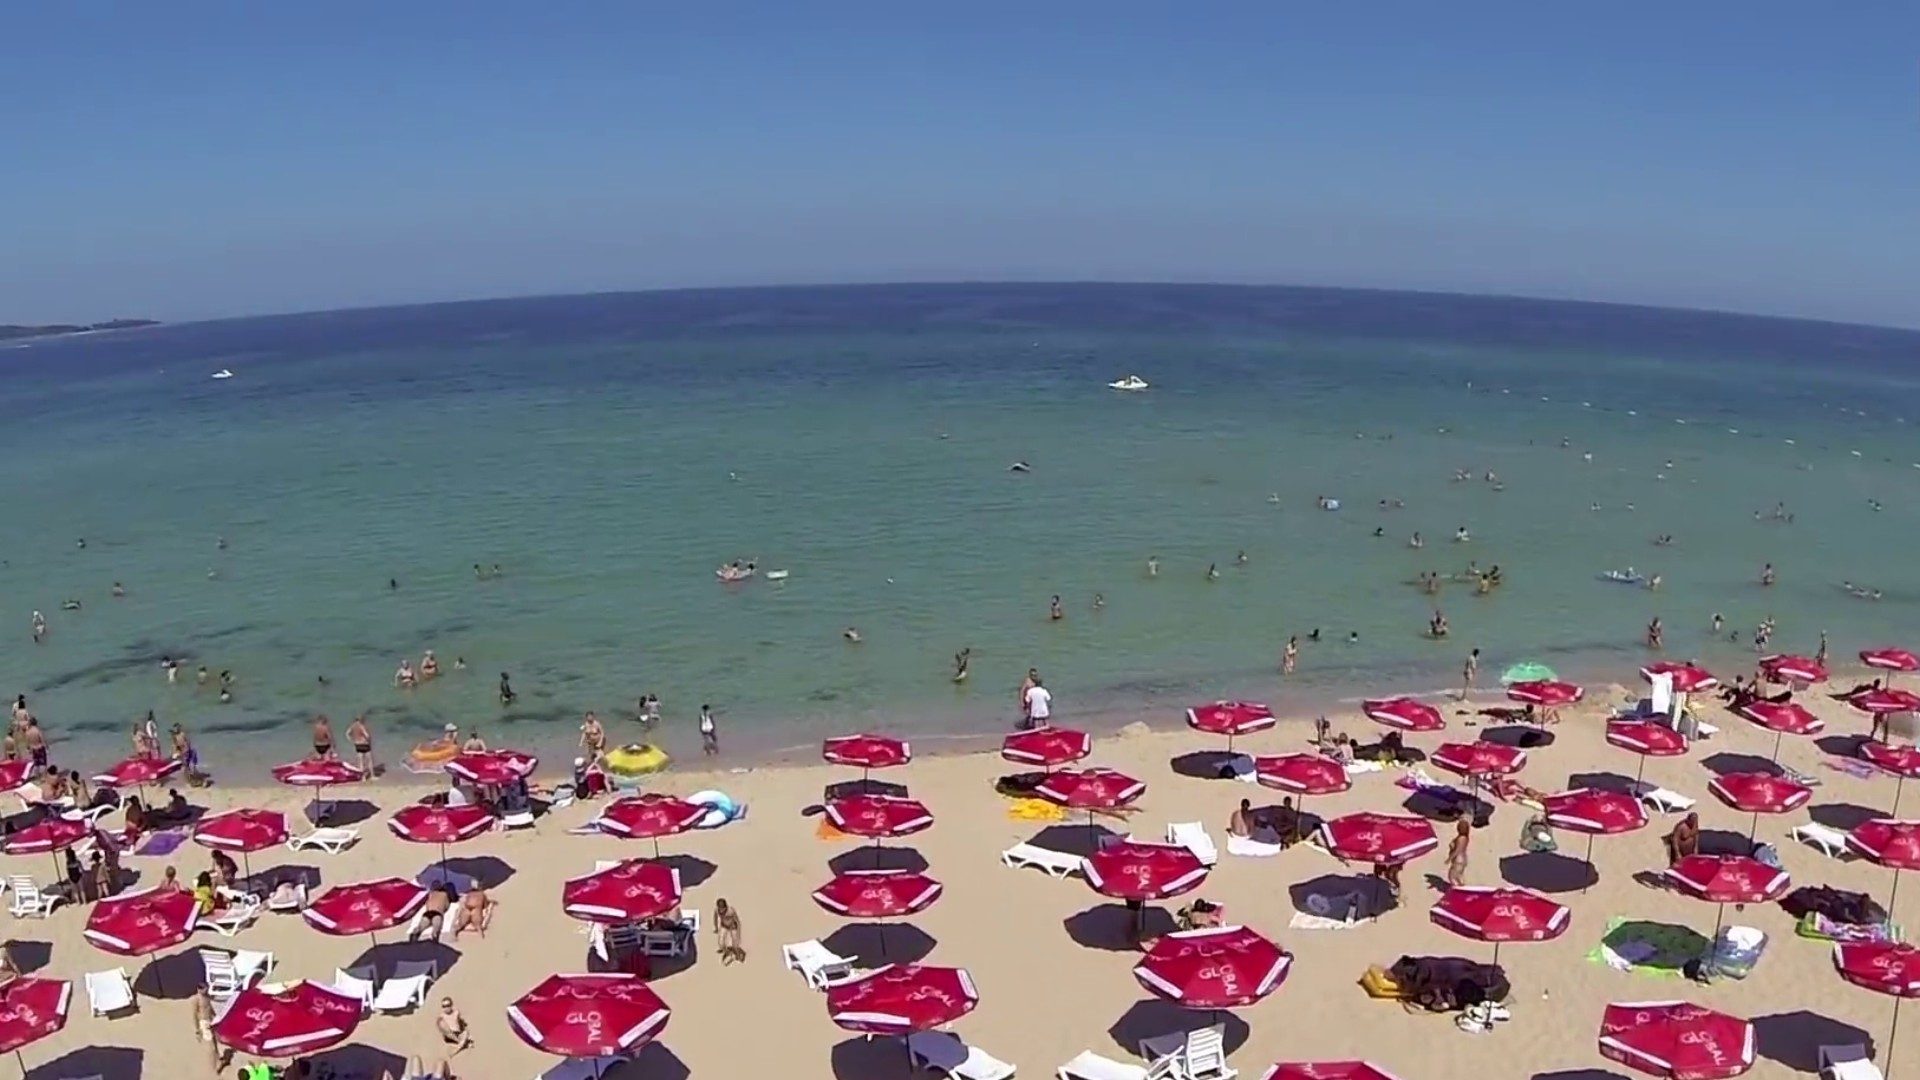
Orios Family Hotel is a three-star retreat 200 metres from Primorsko’s golden beach and the protected Stamopolu dunes. Last renovated in 2024, it offers 90 comfortable rooms, a gre...

Quick Links

arrow_forward Home arrow_forward Rooms & Suites arrow_forward About us arrow_forward Beach & pool arrow_forward Restaurant & bars arrow_forward Events arrow_forward Prices & packages arrow_forward Contact

Contact

phone +359 876 413 400 mail [email protected]
location_on Orios Family Hotel, 9 Lotos St, Primorsko, Bulgaria

© 2026 Orios Family Hotel. All rights reserved.

Powered by HotPilot
Continue booking 0

Семеен Хотел Ориос

powered by HotPilot

Previous chats

Microphone access needed

To talk with the assistant, your browser needs microphone access for this page — right now it's turned off.

Tap the icon on the left of the address bar (a camera, lock, or sliders icon), set the microphone to “Allow”, then reload this page.

✓ Signed in
Thu 15:09
M
Maria
Hi, I'm Maria! I'm here to help with anything about your stay.
  • English
  • Български
  • Deutsch
  • Ελληνικά
  • Română
  • Русский
  • Español

We use cookies to run this site, remember your choices, and measure and improve it. Essential cookies are always on. Cookie Policy